AirCommand
In progress · Personal projectA Wi-Fi auditing tool that wraps aircrack-ng, hashcat and nmap behind one interface, and only acts on networks you’ve allowlisted as authorised to test.
What I did
- My own project. I wrote the scope and the architecture, and I’m building it.
- I’m building it to learn network security. Two bugs I’ve fixed only showed up on real hardware: aircrack-ng never exits if its capture file is shorter than the 24-byte pcap header, and a crash can leave the adapter stuck in monitor mode.
- Team
- Solo
- When
- 2026, in progress
- Built for
- Personal project
The problem
Mature tools like aircrack-ng, hashcat and nmap each run on their own, with their own commands, output and state. AirCommand puts them behind one desktop interface and adds what they leave to the operator: workflow, tracking and authorisation.
What it does
- Management
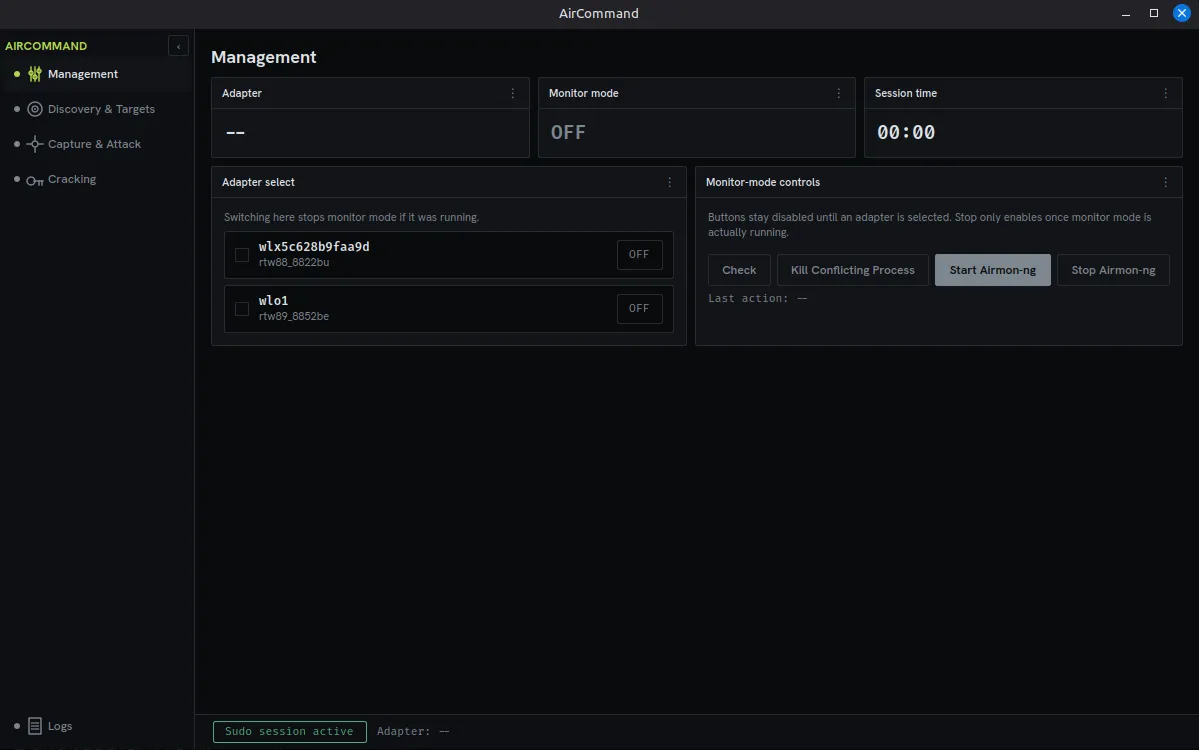
- Picks the Wi-Fi adapter AirCommand uses, switches it while the app is running, and steps its monitor mode by hand: check for conflicting processes, stop them, start or stop monitor mode.
- Discovery
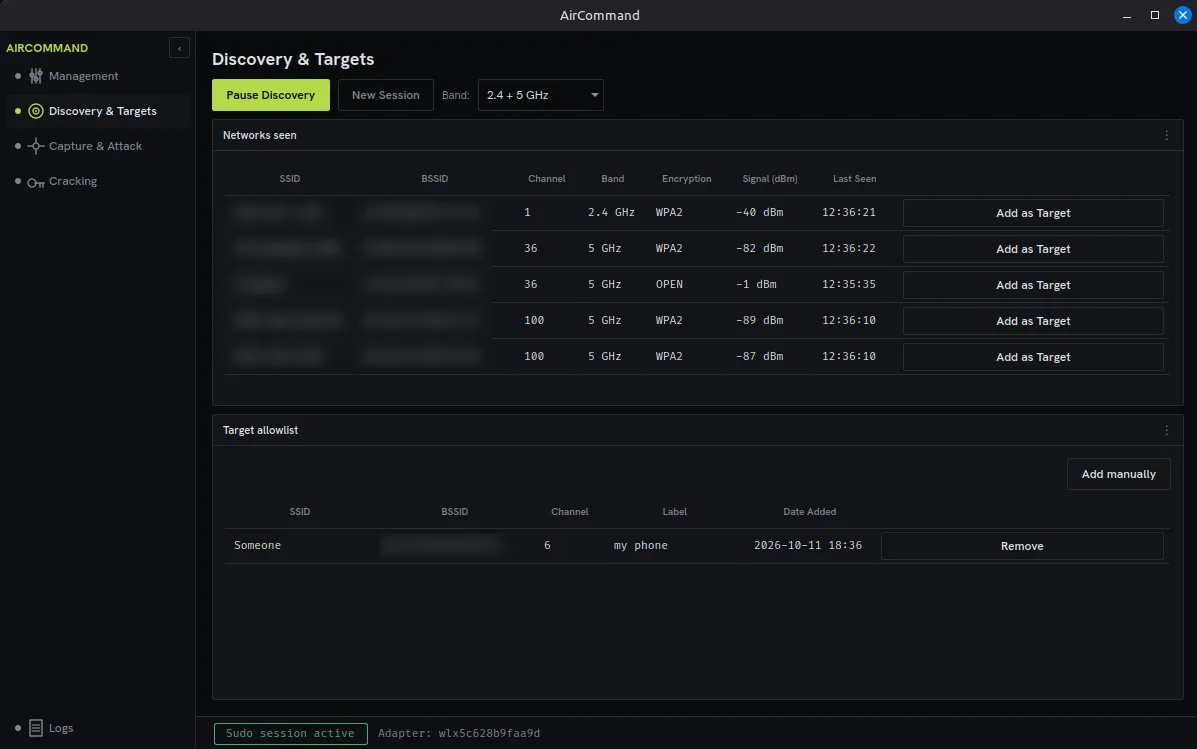
- Lists nearby networks from the beacons it hears, on 2.4 GHz, 5 GHz or both, limited to what the adapter supports. Each network has to be added as a Target on its own; a dual-band router shows up twice and needs two.
- Capture
- Records a WPA handshake from a Target, by listening or by sending deauth frames. Sending deauth frames asks for confirmation every time.
- Enumerate
- Runs an nmap host and port scan against a Target’s subnet, once you have joined that network through the system’s own Wi-Fi settings.
- Crack
- Runs hashcat against a captured handshake and a wordlist you choose. The capture is converted with hcxpcapngtool first, so hashcat can read it. Progress is live, and past attempts are kept.
- Audit log
- Lists every deauth burst fired, for every Target, and never deletes a record. It can be filtered by Target.
How it works
- 01DiscoveryPassive. Sees any network, touches none.
- 02AllowlistThe only thing that can create a Target.
- 03Gated actionsCapture, enumerate, crack. They accept a Target or nothing, one job per radio.
- 04Audit logWritten and committed before anything is reported.
- 01
Only the allowlist makes a Target
Passive discovery can see any network. Any active operation needs a Target, and only the allowlist can create one.
- 02
No code path around the gate
Capture and Enumerate only accept a Target, and Crack only accepts a handshake captured from one. Only the allowlist can create a Target, so no code can point them at any other network.
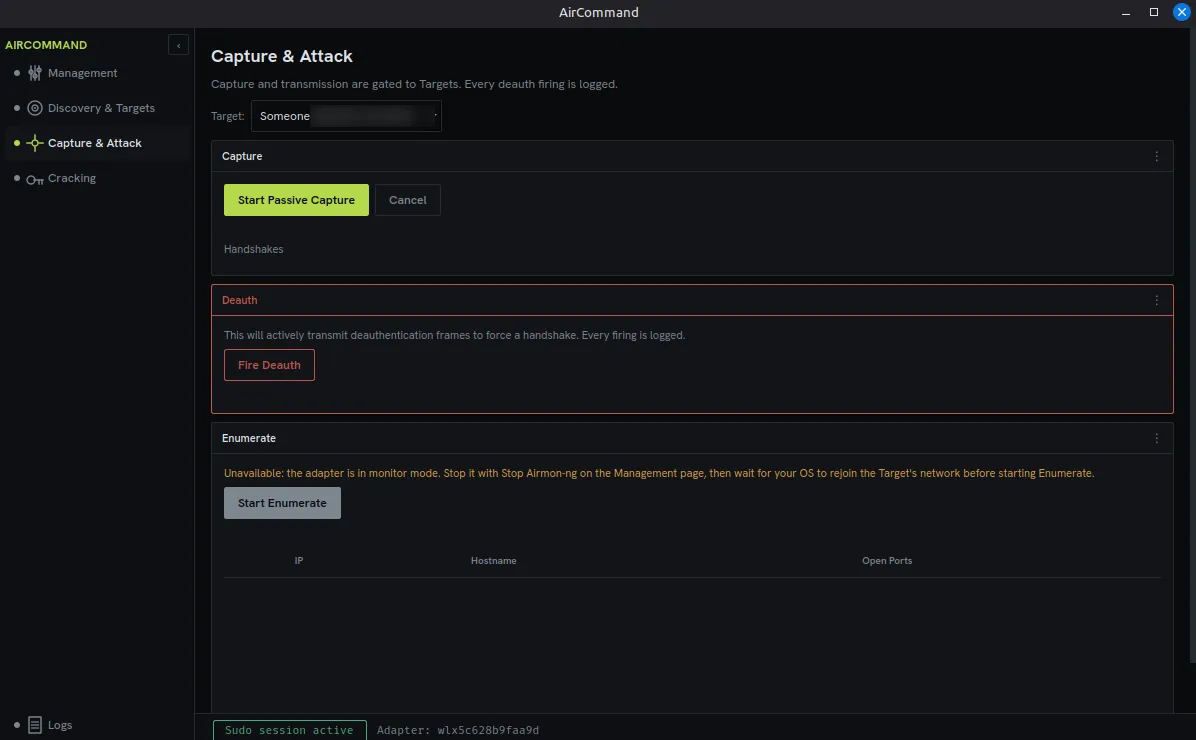
Capture, deauth and enumerate are all scoped to a Target. With no Target, there is nothing to act on. - 03
A thin GUI over an event-driven core
All the work runs in a core Python package with no GUI code in it. The core runs each job and publishes its progress as events; the GUI only displays them.
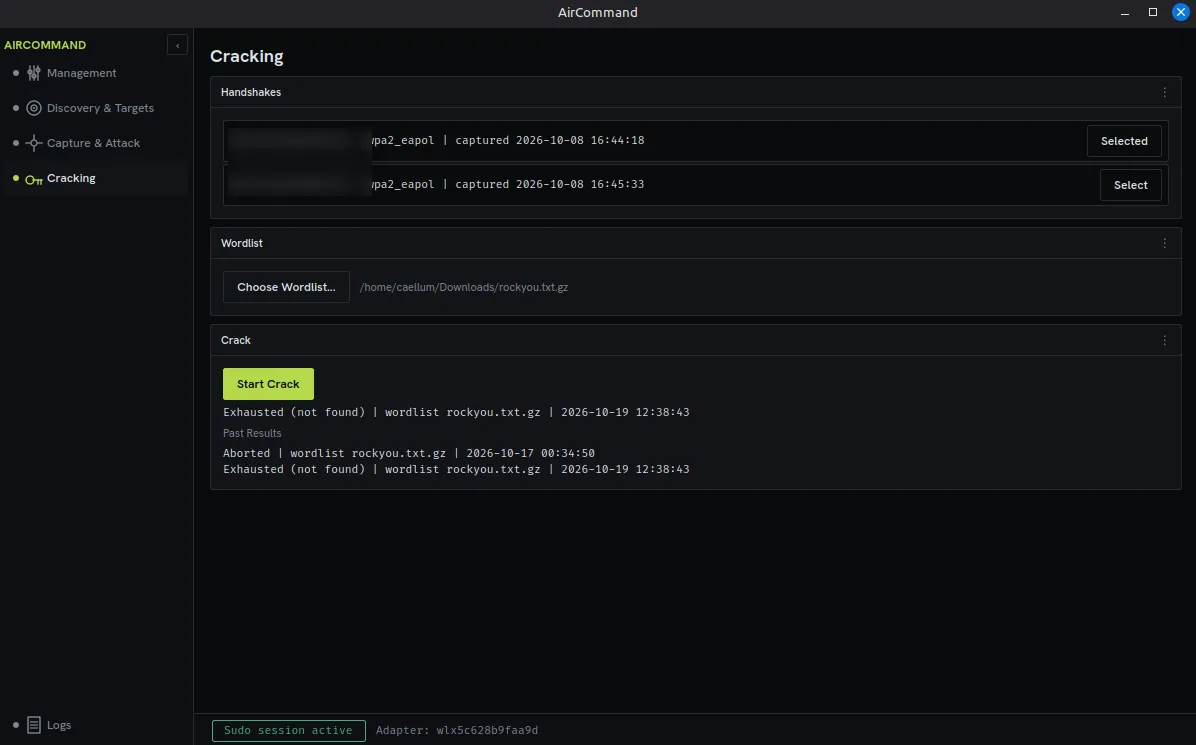
The core runs the hashcat job and streams progress and past results to the GUI. - 04
One radio, one job
The Wi-Fi adapter can run one job at a time. Discovery, Capture and Enumerate each reserve it first, and a second job is refused instead of corrupting the adapter’s state.
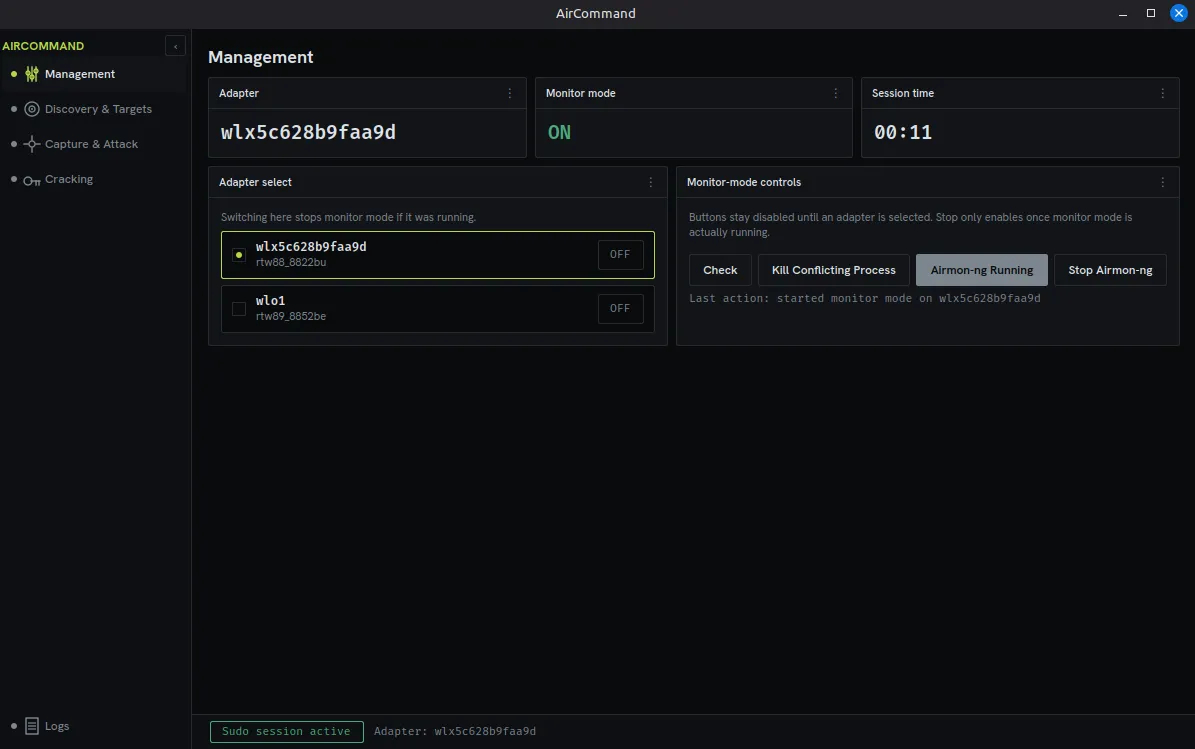
One radio reserved for one job. Monitor mode runs on the chosen adapter; switching adapters stops it first.
Design decisions
- Cut from scope on purpose: WEP cracking, WPS attacks and evil-twin creation. Rogue access point detection stays in.
- One password prompt at launch. Nothing privileged persists once the app closes.
- Every active operation is audit-logged, and only reported once the log write has committed.
- The core is testable with no GUI, no root and no hardware.
More screenshots
Built with
- Python
- Python desktop GUI
- SQLite
- Linux
- Wraps aircrack-ng, hashcat, nmap